 NewMalicious App · iOS
Food-delivery app ComeCome linked to a remote crypto-wallet attack

 At a glance
- Disguise
- Food-delivery app
- Platform
- iOS, iPad and Mac
- Technique
- Remote code poisoning
- Reported by
- SlowMist founder Cos
What happened
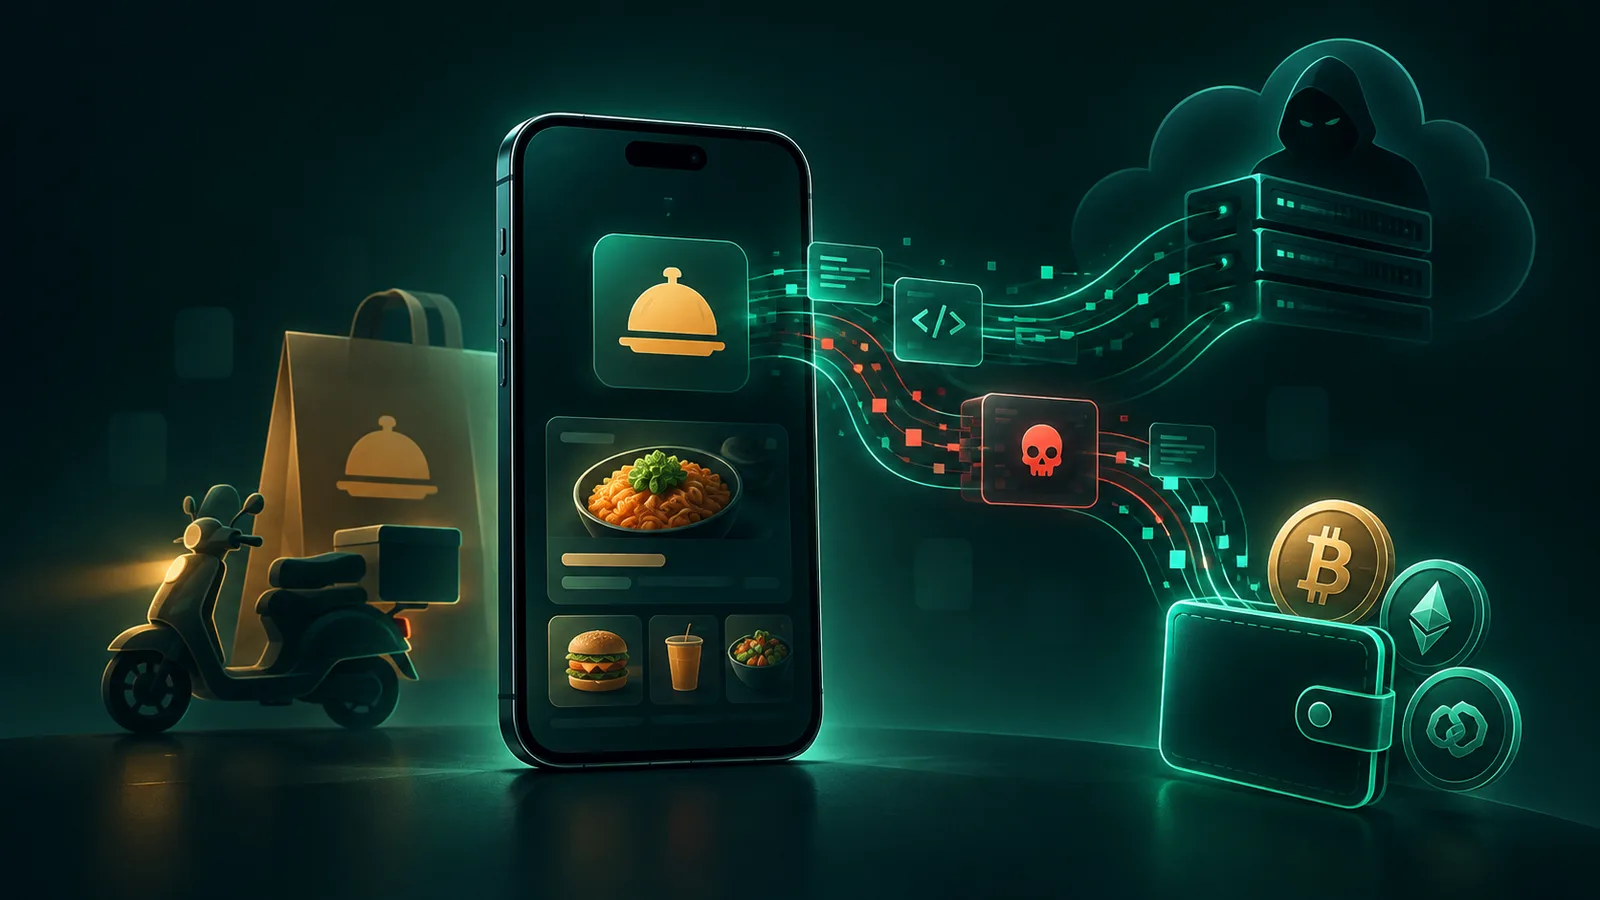
ComeCome appeared to be a food-delivery app, but researchers warned that it used a poisoning technique similar to FomoPeek. After installation, attackers could remotely push code aimed at crypto wallets.
A same-named app also appeared in the 2025 SparkCat report, but the incidents have not been confirmed as the same campaign.
What was found
The risk came from code delivered after installation rather than from the app's visible purpose. That makes normal-looking lifestyle apps a useful disguise for wallet-focused attacks.
Data at risk
- Crypto wallets
- Sensitive data
- Remote payloads
- Account access
- Device security
- Personal data
What you should do
- Update iOS to the latest available version.
- Remove ComeCome if it is installed.
- Avoid apps from unclear sources or with unusual behavior.
 View original postKuCoin · PANews