 NewWeb Attack · Safari
Poisoned web packages could compromise iPhones through Safari

 At a glance
- Entry point
- Safari webpage
- Affected
- iOS 18.4-18.6.x
- Packages
- 13 Composer packages
- Reported by
- Socket / Kush Pandya
What happened
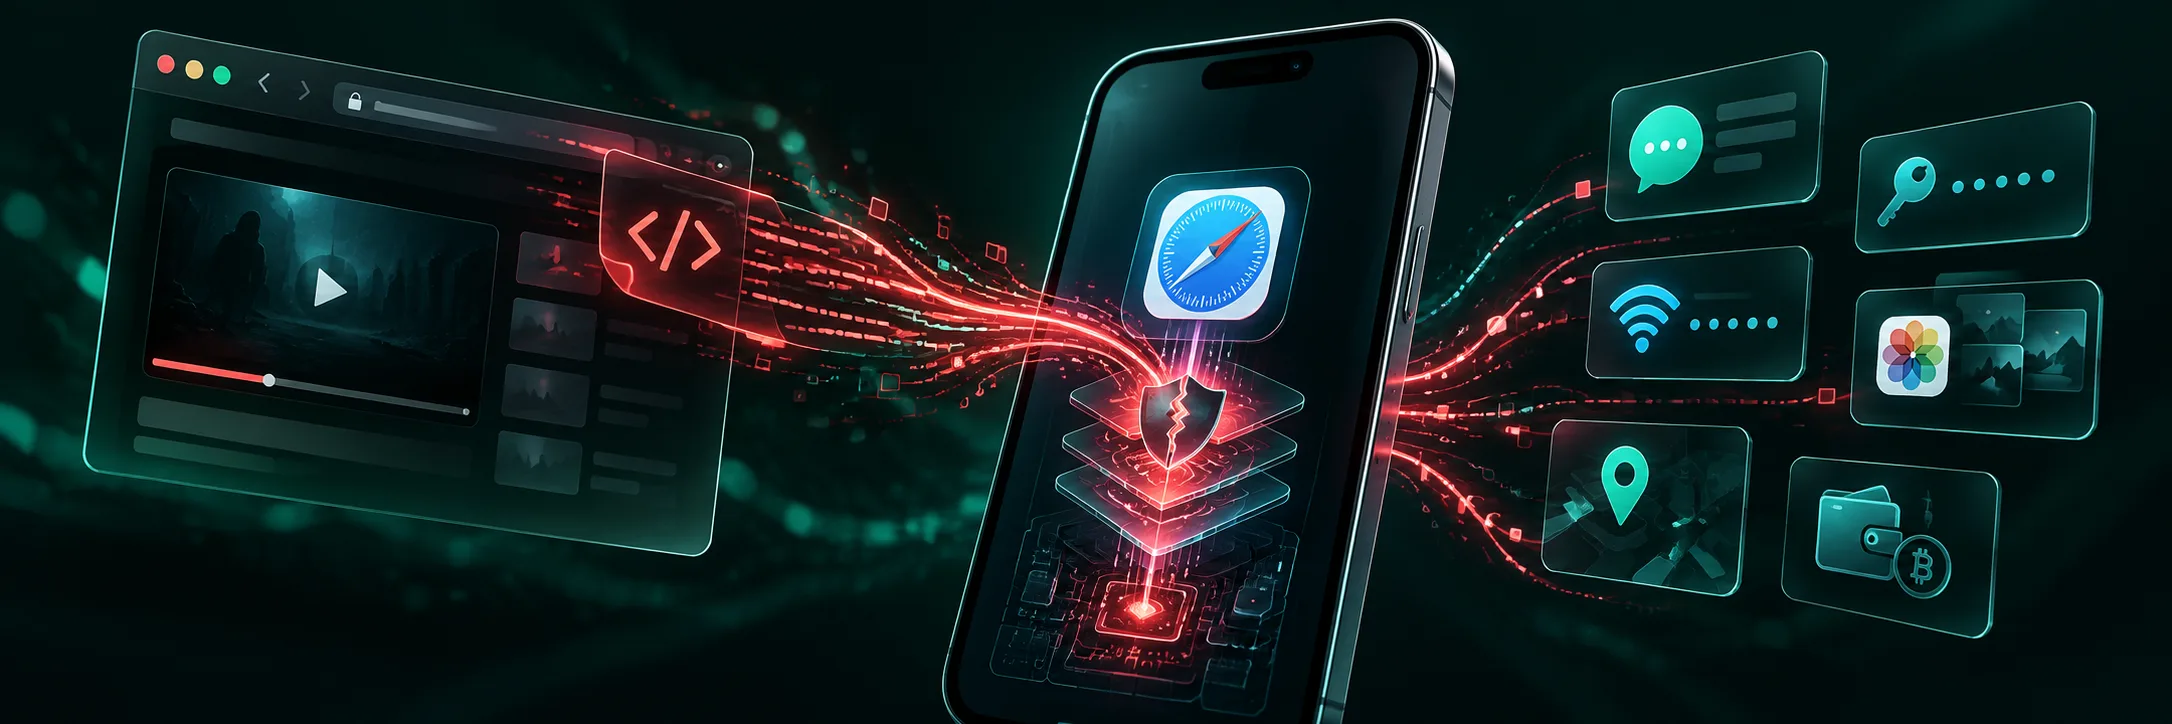
Attackers poisoned open-source Composer packages used by streaming and video sites. An iPhone could be exposed simply by opening a compromised webpage; no malicious app installation was required.
This is the only case in the library where visiting a webpage can start the attack chain.
What was found
Hidden JavaScript detected the iOS version and loaded matching exploits. The chain escaped WebKit and the GPU process before reaching kernel read-and-write access. Apple fixed the kernel escape in iOS 26.1.
Data at risk
- Messages
- Seed phrases
- Wi-Fi passwords
- Keychain data
- Photos
- Location data
What you should do
- Update iOS to version 26.1 or later.
- Avoid unfamiliar streaming and video sites.
- Do not enter sensitive information on suspicious pages.
- Use an isolated hardware wallet if the device cannot be updated.
 View original postThe Hacker News · Socket